Uninstall PC Malware
Uninstall Browser Hijacker
Uninstall Rogue Program
Uninstall ransomware
Uninstall Trojan Virus
Uninstall malicious adware.
Uninstall Rogue Program
Uninstall ransomware
Uninstall Trojan Virus
Uninstall malicious adware.
Uninstall PC Malware helps Internet users remove malicious viruses and upgrade PC performance
Fix PC errors
Fix device driver problems
Speed up computer
Upgrade PC performance.
Fix device driver problems
Speed up computer
Upgrade PC performance.



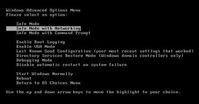 1. Here is how: Start the infected computer by pressing the power button or clicking the Restart option on the Start menu. And then hit F8 key on the keyboard before the Windows launches. It will bring you to the Windows Advanced Options menu where says safe mode, safe mode with networking, safe mode with command prompts. What you should do now is highlight safe mode with networking option and hit enter key. Later after that, Windows will be loading files and then desktop may show up.
2. Open Windows Task Manager: By pressing Shift+ Ctrl+ Esc keys to reveal Windows Task Manager dialog. And click on Process tab. Find and click on the malicious process and click on end process. If you are using window XP and Windows 8, you can press Ctrl+ Alt+ Del to access to the Windows Task Manager. Later after that you can end the VBS/Dinihou.G.2 virus malicious process.
How to Remove VBS/Dinihou.G.2 Trojan Virus Completely?
VBS/Dinihou.G.2 is regarded as malicious Trojan virus, which can make the infectious computer totally vulnerable and then steal sensitive information there. The VBS/Dinihou.G.2 virus is designed by hijackers focuses on acquiring malicious benefits. VBS/Dinihou.G.2 virus is quite infamous computer infection that threatens both of the infectious system and privacy. This virus pretends to be a needed executable files and complied in system to conceal its existence so that it can be stubborn on the infectious machine. VBS/Dinihou.G.2 virus must constantly exploit system vulnerabilities to the compromised machine, as doing so can hijacker access to the victimized machine through backdoor. Once hijackers accessed in the infectious system, they will try efforts to steal confidential data such as log-in credentials, banking data, or Credit Card number.
VBS/Dinihou.G.2 virus can accomplishedly infect a virus just through drive-by downloads including freeware, shareware, or web plugins. Hijackers frequently hide such VBS/Dinihou.G.2 virus in those third-party Windows programs. Just when users are downloading those potentially unwanted programs the VBS/Dinihou.G.2 virus can entice in the targeted machine simultaneously. In addition, such Trojan virus still can attack computer through spam emails and pop-ups. It can run on Windows boot-up and carry out dangerous activities without any distraction. Although you have installed anti-virus program on your computer to fight against virus, the VBS/Dinihou.G.2 virus still can bypass it and even disable it. Therefore, you can’t identify it until the VBS/Dinihou.G.2 virus self appears on the infectious screen.
Tips: In case of further damage, you’d better remove the VBS/Dinihou.G.2 virus from the infectious machine completely. You can use VilmaTech Online Services – The Global PC Support Center.
VBS/Dinihou.G.2 is regarded as malicious Trojan virus, which can make the infectious computer totally vulnerable and then steal sensitive information there. The VBS/Dinihou.G.2 virus is designed by hijackers focuses on acquiring malicious benefits. VBS/Dinihou.G.2 virus is quite infamous computer infection that threatens both of the infectious system and privacy. This virus pretends to be a needed executable files and complied in system to conceal its existence so that it can be stubborn on the infectious machine. VBS/Dinihou.G.2 virus must constantly exploit system vulnerabilities to the compromised machine, as doing so can hijacker access to the victimized machine through backdoor. Once hijackers accessed in the infectious system, they will try efforts to steal confidential data such as log-in credentials, banking data, or Credit Card number.
VBS/Dinihou.G.2 virus can accomplishedly infect a virus just through drive-by downloads including freeware, shareware, or web plugins. Hijackers frequently hide such VBS/Dinihou.G.2 virus in those third-party Windows programs. Just when users are downloading those potentially unwanted programs the VBS/Dinihou.G.2 virus can entice in the targeted machine simultaneously. In addition, such Trojan virus still can attack computer through spam emails and pop-ups. It can run on Windows boot-up and carry out dangerous activities without any distraction. Although you have installed anti-virus program on your computer to fight against virus, the VBS/Dinihou.G.2 virus still can bypass it and even disable it. Therefore, you can’t identify it until the VBS/Dinihou.G.2 virus self appears on the infectious screen.
Tips: In case of further damage, you’d better remove the VBS/Dinihou.G.2 virus from the infectious machine completely. You can use VilmaTech Online Services – The Global PC Support Center.
 3. Delete VBS/Dinihou.G.2 virus files. Show hidden files first: Click Start button->Go to Control Panel->Double click on Files and Folder Option->Select View tab->Check “Show hidden files, folders and drives”->Uncheck “Hide protected operating system files (Recommended)-> Click Ok. Then open local disk to delete virus files. The virus files are in same form as the one: %AllUsersProfile%random.exe. To open local disks, you can double click on My Computer icon on the desktop.
4. Delete registry entries: Press Windows + R keys and enter regedit in Run window, click Ok. In Registry Editor, search the VBS/Dinihou.G.2 virus and delete related registry entries.
HKEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionRun “.exe”